Secure electronic signature: how to tell whether yours will hold up
A secure electronic signature takes more than a padlock icon. Check signer authentication, tamper evidence, audit trails and certifications before you choose.
Sign a document and check the record yourself.
Start nowWhat a secure electronic signature has to prove
A secure electronic signature is one you can defend a year from now, in front of someone with a reason to doubt it. The padlock in your browser doesn't tell you that. Neither does a vendor's homepage.
When a signature is challenged, the questions are nearly always these four:
- Who signed? Not which email address clicked, but which person.
- What did they sign? The exact version, down to the last byte.
- When did each step happen, and in what order?
- Has anything changed since?
Security people call the result non-repudiation: the signer can't credibly deny the act, because the evidence ties a person to a specific file at a specific moment.
Here's the uncomfortable part. Most signing tools get the cryptography right. They differ on how hard they check the signer, what they log and whether the evidence survives without them. Signing a document in Chaindoc takes minutes; this page is about whether you'd trust the result in a dispute.
The numbers behind the risk
From the FBI's 2024 Internet Crime Report and Verizon's 2025 Data Breach Investigations Report, read on 14 October 2026. They count fraud and breaches in general, not signature fraud.
- Losses reported to the FBI in 2024
- $16.6 billion
From 859,532 complaints, a 33% rise on 2023 (FBI IC3, 2024 report).
- Phishing and spoofing complaints, 2024
- 193,407
The most-reported crime type of the year (FBI IC3, 2024 report).
- Business email compromise losses, 2024
- $2.77 billion
Across 21,442 complaints, often inside a real contract or invoice thread (FBI IC3).
- Breaches with a third party involved
- 30%
Up from 15% a year earlier (Verizon 2025 DBIR).
Are electronic signatures safe? The risk sits around the signature
Yes, in the narrow sense. Nobody fakes a properly made digital signature by breaking the maths behind it. The attacks that work go around it: someone gets into the signer's inbox, a fake signing request harvests a password, or a supplier in the chain gets breached.
None of the figures above is about signatures as such. They describe the channel signing runs through: email, invoices, outside vendors. So the useful question about a secure electronic signature isn't how strong the encryption is. It's how the signer gets checked, and what happens when a request looks real but isn't.
What a secure electronic signature can't fix
It can't stop someone who's talked into signing a document they didn't read, and it won't notice a bank account swapped in a follow-up email. Those are process problems. A call to a number you already had does more against them than any signing feature.
Electronic signature authentication: how sure are you of the signer?
Plenty of signing requests still work like this: a link arrives by email, the recipient clicks it, types a name, done. That proves somebody could read that inbox at that moment. For a holiday request, fine. For a contract someone might later disown, it's thin.
NIST is blunt about it. Its 2025 guidelines, SP 800-63B-4, say email shall not be used for out-of-band authentication, treat SMS and voice codes as restricted, and require services at the middle assurance level to offer a phishing-resistant option. Those rules govern US federal systems, not your sales contracts. They're still the most careful public ranking of the methods signing tools offer.
Signer authentication methods, from weakest to strongest
| Method | What it proves | Weak point | Where it fits |
|---|---|---|---|
Email link only | Someone could open that inbox | Shared or hijacked mailboxes; NIST rules email out | Internal approvals, low-value forms |
Access code you share separately | The signer got a code passed on another way | Only as strong as that other channel | Counterparties you already know |
SMS or voice one-time code | Control of a phone number | SIM swaps; NIST lists phone codes as restricted | Consumer agreements, mid-value deals |
Knowledge-based questions | The signer knows facts about themselves | Answers often sit in breached data | Older US financial forms |
Government ID plus live selfie | A real person matching an ID document | Takes a minute and needs a camera | Property, lending, hiring, large contracts |
Qualified certificate (QES) | Identity verified by a supervised trust provider | Cost and setup; built around EU law | Where EU law or the other party demands it |
An email link proves access, not identity
If a forwarded email is all that stands between a stranger and your contract, that's the whole security model. Shared inboxes such as sales@ make it worse, because the record shows whoever clicked. Ask any provider what it records about how each signer was checked. If the answer is an IP address and a timestamp, assume a court will read it the same way.
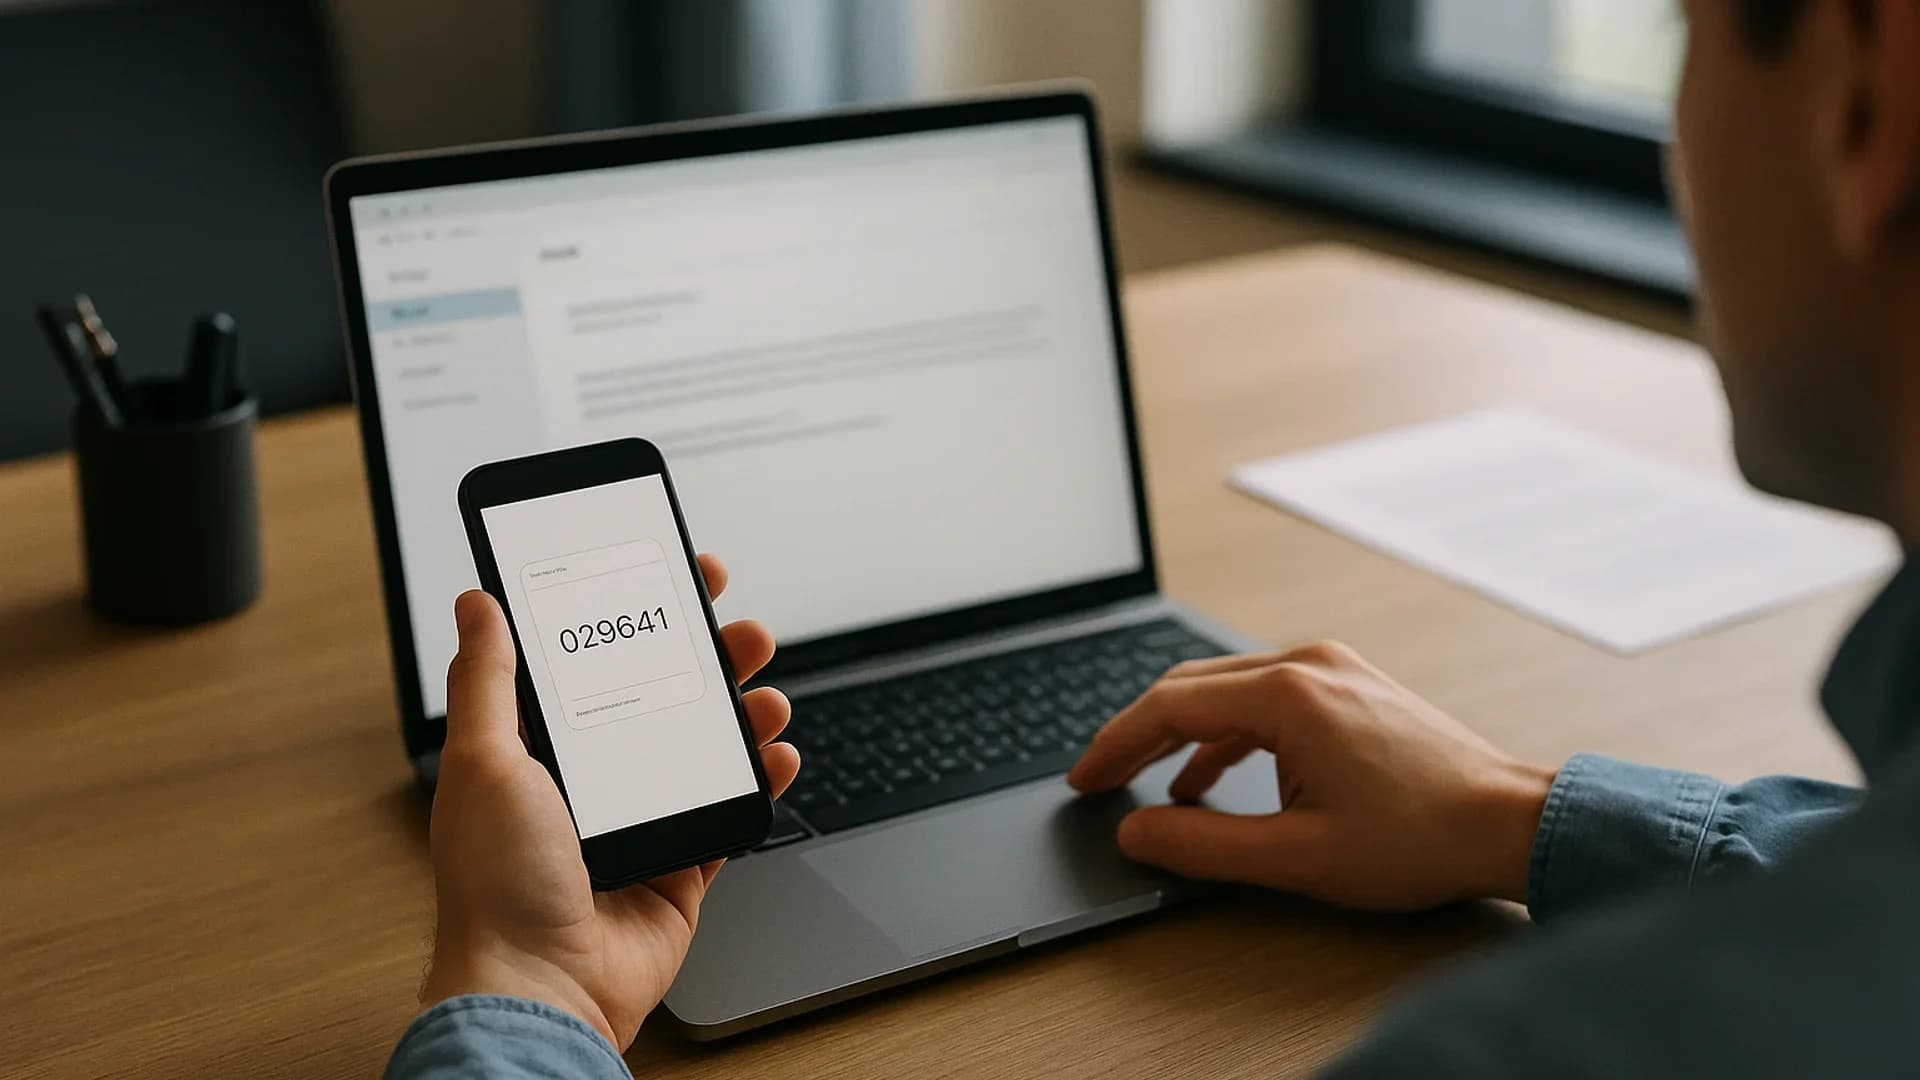
A second channel raises the bar above a bare email link. On its own, it still isn't proof of who signed.
Tamper evidence: how a secure electronic signature locks the file
Underneath a secure digital signature, the software runs the document through a hash function, which gives a short fingerprint unique to that exact file. Change one comma and the fingerprint changes completely. That fingerprint is signed with a private key whose certificate comes from a public key infrastructure (PKI), and the result is embedded in the PDF. Any PDF reader can recompute it later. Match: it's the signed document. No match: the reader flags it.
You can test a provider in five minutes:
- 1.Open a file it has signed in Adobe Acrobat Reader or another PDF reader and look at the signature panel. You should see who sealed it and whether it changed since.
- 2.Edit one character in a copy, save it and reopen it. A properly sealed file now flags the signature as invalid or the document as altered.
If the panel is empty, you're holding a picture of a signature plus a log on the vendor's server. That can still be legally valid, but all of the proof lives with the vendor.
What the audit trail behind a secure electronic signature records
The signature proves the file didn't change. The audit trail proves everything around it, and when a secure electronic signature is disputed, it's usually the trail that gets read aloud. A complete one records at least:
- Each signer's identity and how it was verified: email only, a code, an ID check.
- A timestamp for every step, from sending through viewing to signing, with the time source stated.
- IP address and device details for each action.
- The document's fingerprint for each version, so the record ties to the file you hold.
- What the signer agreed to, including consent to sign electronically.
- Who sent the request, plus reminders, declines and voided versions.
Then ask two things. Can you export the trail as a file you keep? Could the vendor change it later without leaving a mark? A trail kept only in an editable database is evidence you take on trust. Our guide to what a complete audit trail contains walks through each field.
Non-repudiation: when a signer says 'that wasn't me'
Non-repudiation stops a signer from credibly denying they signed. In security textbooks it comes from the cryptography: only the holder of a private key could have produced this signature. In a courtroom it's messier. The key proves a device or account was used; the argument then moves to whether the person behind it is who they claim. That's why signature law sets a low bar for validity and leaves the rest to evidence.
United States
The ESIGN Act, at 15 U.S.C. § 7001, says a signature or contract can't be denied legal effect solely because it's electronic. It names no technology, and its retention rule asks that the record reflect the contract accurately and stay accessible in a reproducible form. State-level UETA works the same way; New York, which never adopted it, has its own Electronic Signatures and Records Act. None of them tells you how to prove who signed. That falls to your evidence.
European Union
eIDAS Article 25 says an electronic signature can't be refused as evidence just because it's electronic or not qualified, and gives a qualified signature the effect of a handwritten one. Article 26 defines the advanced level in between: uniquely linked to the signer, able to identify them, made with data under their sole control, and linked to the document so any later change is detectable. Most EU business contracts are signed at the simple or advanced level, and that's legally fine. The difference shows when someone objects. In Germany, France and Spain, national law presumes a qualified signature genuine until shown otherwise; at the other levels, you're the one who shows it's right.
United Kingdom
Section 7 of the Electronic Communications Act 2000 makes an electronic signature admissible as evidence of a document's authenticity and integrity. Admissible isn't the same as convincing.
So non-repudiation isn't a feature you buy. It's the sum of how the signer was checked, how the file was sealed and what was logged, and it's as strong as the weakest of the three.
See what a signed file actually carries
Sign a document in Chaindoc and open it in any PDF reader. The signature, the audit trail and the on-chain record stay with you.
Try signing a documentHow to check a provider's security certifications
Every vendor selling a secure electronic signature shows a row of badges on its security page. Treat them as claims to check; it takes about ten minutes a vendor.
ISO 27001
ISO 27001 certifies an information security management system, audited by an accredited body on a cycle. Look the certificate up in IAF CertSearch, the database of accredited certificates. Check that it's current, who issued it and its scope, since it can cover one office rather than the service you're buying.
SOC 2 Type 2
SOC 2 is an auditor's attestation report, common among US vendors and often required by US buyers. Type 2 covers how controls operated over months; Type 1 describes them on one date. Expect to sign an NDA to see it, then read the period, the systems in scope and the exceptions, where the real findings sit.
Qualified trust services
For qualified signatures in the EU, the provider or its certificate partner must be on the EU Trusted List. Our explainer on how the EU Trusted List works shows where to look.
One more question most electronic signature providers skip on their websites: where is the data stored, and which subprocessors touch it? In the EU, the data processing agreement should name them.
Is DocuSign secure? Mostly, and the weak spot is your inbox
On certifications, DocuSign is ahead of Chaindoc. Its compliance page lists enterprise-wide ISO 27001:2022 certification, SOC 1 Type 2 and SOC 2 Type 2 reports, and PCI-DSS (read on 14 October 2026). If procurement insists on SOC 2, that's a genuine reason to shortlist it.
The risk people actually meet is an email pretending to be DocuSign, because a familiar request rarely gets a second look. DocuSign's safety page says real requests come from official domains such as docusign.net, never arrive as file attachments, and carry a security code for opening the document on its website instead of the link. For the legal side, see DocuSign's standing in court.
Will your secure electronic signature outlive the provider?
Vendors get acquired, change plans and close accounts. Contracts often outlast all three. So ask: if this company vanished tomorrow, what could I still prove?
A good answer has two parts. The signed PDF carries its own signature, which any PDF reader can check. And the audit trail is a file you've downloaded, rather than a page in someone else's dashboard.
Some providers give a secure electronic signature an independent anchor as well. Chaindoc writes the fingerprint of a document version to a public blockchain when you publish it for signing, then records each signer's proof there on completion. Anyone with the transaction link can look it up on a public block explorer, whether or not Chaindoc's servers are running. Our PDF signature verification service reads the signatures embedded in a signed file.
One limit worth knowing: certificates expire, and old signatures validate best when the file also carries a trusted timestamp and validation data, which the PAdES levels above the baseline add. Chaindoc's signatures are PAdES-BES, the baseline without a timestamp, so for decade-long retention keep the audit trail and verification report with the file. Ask any provider which PAdES level it produces.
Blockchain doesn't make a signature legal
ESIGN, UETA and eIDAS don't require a blockchain, and a signature is valid without one. What it adds is an integrity record neither you nor the vendor can quietly edit. Chaindoc puts the document fingerprint and each signer's proof on chain; the file itself never goes there, and neither do the signers' identities. It helps most when the vendor's own records are what's being questioned.
A secure electronic signature checklist for comparing providers
Put your shortlisted electronic signature providers through the same seven questions. Most lists of the best eSignature software rank tools on price and integrations; these rank them on what you could prove later. For the cost side, see our guide to comparing e-signature software on price and features.
Seven questions to put to any e-signature provider
| Question | A good answer | A red flag |
|---|---|---|
How is each signer authenticated, and per document? | Several methods, set per document | Email link only, for everything |
Does the signed PDF carry its own signature? | Yes, visible in any reader's signature panel | An image plus a log on the vendor side |
Can I export the audit trail as a file? | A PDF per document | Viewable only inside the account |
Which PAdES level, and is there a trusted timestamp? | A named level and a straight answer | No answer, or "bank-grade security" |
Which certifications, and can I verify them? | Certificates you can check with the issuer | Badges with nothing behind them |
Where is data stored, and by which subprocessors? | A named region and a list in the contract | "In the cloud" |
What happens to my records if I cancel? | An export window and retention terms in writing | Evidence deleted with the account |
Chaindoc's secure electronic signature: what it does and doesn't do
Here's where we stand against that checklist, gaps included.
Chaindoc holds ISO 27001 and ISO 9001 certificates, both listed in IAF CertSearch. We don't have a SOC 2 report; if your buyer requires one, that's a real gap, and better you hear it from us.
Signatures are advanced electronic signatures in PAdES-BES format, embedded in the PDF. Files travel over TLS, and users' private signing keys are encrypted with AES-256. It isn't end-to-end encrypted: the server reads each file to scan it for malware and apply the signature. The server fingerprints a file on upload; that fingerprint goes on chain when you publish, and each signer's proof follows on completion. The audit trail and a verification report download as PDFs.
On paid plans, the optional identity check adds a government ID and live selfie inside the signing flow, switched on per document. For qualified signatures you bring a certificate from a qualified trust service provider; Chaindoc runs the signing flow but isn't one itself. A fixed signing order runs through approval routes on the Business plan (see plans and pricing).
If that fits how you sign, creating a secure electronic signature takes a few minutes. If you need a SOC 2 report or long-term validation built into the file today, another provider will serve you better.
Sources checked for this guide
We read each page on 14 October 2026. Statutes link to the official or a standard legal text, vendor facts to the vendor's own page.
- 1.2024 Internet Crime Report · FBI Internet Crime Complaint CenterTotal losses of $16.6 billion from 859,532 complaints; phishing and spoofing 193,407 complaints; business email compromise losses of $2,770,151,146 across 21,442 complaints. Checked 2026-10-14.
- 2.2025 Data Breach Investigations Report, executive summary · VerizonThird-party involvement in breaches doubled from 15% to 30%; the human element stayed around 60%. Checked 2026-10-14.
- 3.SP 800-63B-4, Digital Identity Guidelines: Authentication and Authenticator Management · NISTFinal July 2025. Email shall not be used for out-of-band authentication; phone (PSTN) codes are restricted; AAL2 verifiers shall offer a phishing-resistant option. Checked 2026-10-14.
- 4.15 U.S. Code § 7001, General rule of validity · Cornell Legal Information InstituteESIGN: no denial of legal effect solely because a signature or record is electronic; subsection (d) on accurate, accessible retention. Checked 2026-10-14.
- 5.Electronic Transactions Act · Uniform Law CommissionThe uniform act behind state-level UETA enactments. Checked 2026-10-14.
- 6.Regulation (EU) No 910/2014 (eIDAS), consolidated text · EUR-LexArticle 25 on the legal effect of electronic signatures; Article 26 on the four requirements for advanced electronic signatures. Checked 2026-10-14.
- 7.Electronic Communications Act 2000, section 7 · legislation.gov.ukElectronic signatures are admissible in evidence on a document's authenticity and integrity. Checked 2026-10-14.
- 8.Docusign compliance · DocusignLists enterprise-wide ISO 27001:2022 certification, SOC 1 Type 2, SOC 2 Type 2 and PCI-DSS. Checked 2026-10-14.
- 9.Docusign safety center · DocusignOfficial sending domains such as docusign.net, no signature requests sent as files, the per-email security code, and verify@docusign.com for reports. Checked 2026-10-14.
- 10.Chaindoc ISO 27001 certificate · IAF CertSearchChaindoc's information security management certification. Checked 2026-10-14.
- 11.Chaindoc ISO 9001 certificate · IAF CertSearchChaindoc's quality management certification. Checked 2026-10-14.
Frequently Asked Questions
Answers to popular questions about Chaindoc and secure document workflows.
Yes, when the signature is cryptographically sealed and the signer is properly checked. Attacks rarely break the signature itself; they go after the signer's inbox or send fake signing requests. Choose the authentication level to fit the document, and keep the audit trail.
It means the signer can't credibly deny having signed. In an electronic signature it comes from three things together: how the signer was authenticated, a seal that shows the file hasn't changed, and an audit trail of each step. A key alone proves a device or account was used; the other two tie that use to a person and a document.
Integrity means the document hasn't changed since it was signed, and a hash in the signature proves that. Non-repudiation goes further: it ties the signature to a particular person, so they can't plausibly say someone else did it. You can have integrity without non-repudiation, for instance a sealed file signed from a shared inbox.
On paper, yes: its compliance page lists ISO 27001:2022, SOC 1 Type 2, SOC 2 Type 2 and PCI-DSS. The practical risk is fake emails that imitate it. DocuSign says real requests come from official domains such as docusign.net, never arrive as file attachments, and carry a security code you can use on its website instead of the link.
Check the sender's domain against the vendor's official one, and be suspicious of any request that comes as an attachment or asks for your email password. Hover over the link before you click. Better still, open the vendor's site directly and use the access or security code from the email. If the request is unexpected, confirm with the sender through a channel you already had, such as a known phone number. Report fakes to the vendor.
More e-signature and blockchain guides
Practical guides on electronic signatures, blockchain audit trails, and secure document management — handpicked to build on what you just read.